MUIS says human resource management system hit by cybersecurity incident - CNA
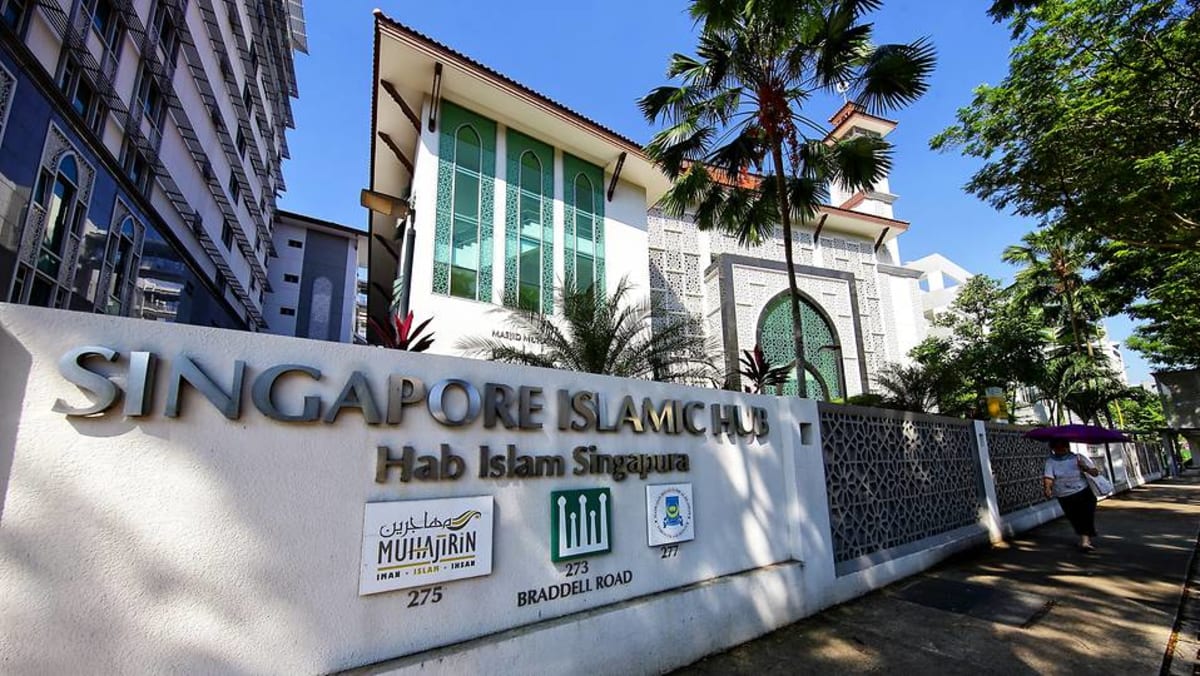
MUIS said the incident does not affect the delivery of public-facing or government services.
Exterior of the Islamic Religious Council of Singapore (MUIS) building. (Photo: Majlis Ugama Islam Singapura)
This audio is generated by an AI tool.
Emil Chan 15 Sep 2026 11:15PM (Updated: 16 Sep 2026 03:13AM) Bookmark Bookmark Share WhatsApp Telegram Facebook Twitter Email LinkedIn Set CNA as your preferred source on Google Add CNA as a trusted source to help Google better understand and surface our content in search results. Read a summary of this article on FAST. Get bite-sized news via a newcards interface. Give it a try. Click here to return to FAST Tap here to return to FAST FAST SINGAPORE: The Islamic Religious Council of Singapore (MUIS) has been hit by a cybersecurity incident involving a human resource management system operated by Singapore-based software vendor Avelogic.
It is working closely with the affected organisations, Avelogic and the relevant authorities on the necessary next steps, said MUIS in response to CNA queries on Tuesday (Sep 15).
The incident does not affect the delivery of public-facing or government services, it added.
“Business continuity arrangements have been implemented to support essential HR and payroll functions, and affected employees are being provided with the necessary guidance and support,” Muis said.
CNA Games Guess Word Crack the word, one row at a time Buzzword Create words using the given letters Mini Sudoku Tiny puzzle, mighty brain teaser Mini Crossword Small grid, big challenge Word Search Spot as many words as you can Show More Show Less MUIS declined to give further information, citing ongoing investigations.
It did not specify how many people were affected or what information may have been compromised.
The Singapore Police Force confirmed with CNA that a report was lodged and that investigations are ongoing.
Separately, Avelogic has published a cybersecurity incident notice on its website concerning its SmartHRMS system.
In an update dated Monday, the company said an independent forensic investigation had found no evidence of bulk data exfiltration, based on available Amazon Web Services network telemetry covering confirmed threat actor activity from Aug 30 to Aug 31.
Avelogic did not identify the customers affected in the notice.
On its website, the company described the SmartHRMS system as "Singapore's CPF-compliant payroll and HR management system for SMEs - automating payroll, leave, claims, employee self-service and attendance in one integrated cloud platform".
The company said in the cybersecurity incident notice that core sensitive data fields within SmartHRMS remained protected by application-layer encryption.
Avelogic filed a police report on Aug 31 and notified the Personal Data Protection Commission in its capacity as a data intermediary.
It commissioned cybersecurity firm Black Panda on Sep 3 to conduct an independent forensic investigation.
The firm added that it successfully recovered the last updated data set, and was aiming to get its new system up by Friday.
“Other components of the system will be brought back online progressively thereafter,” said Avelogic.