Nearly 100,000 Bee Cheng Hiang customers' email addresses exposed in first AI-related data breach in Singapore - CNA
The incident was caused by a human error in developing the email distribution code with an AI tool, the Personal Data Protection Commission said.
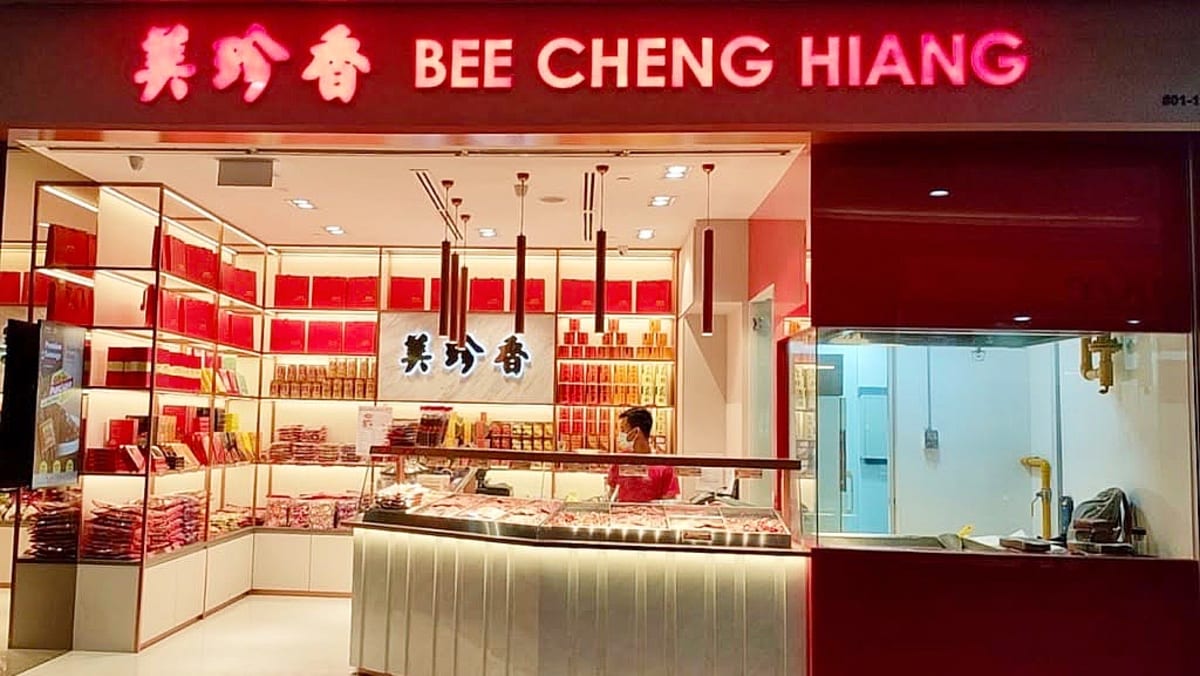
A Bee Cheng Hiang shop near Lavender MRT station. The retailer is known for its barbecued meat products. (Photo: Facebook/Bee Cheng Hiang Singapore)
This audio is generated by an AI tool.
SINGAPORE: The email addresses of nearly 100,000 Bee Cheng Hiang customers were disclosed without consent in what the Personal Data Protection Commission said on Wednesday (Sep 30) was the first AI-related data breach in Singapore that it has been notified of.
The breach occurred in April after a Bee Cheng Hiang employee used an AI tool to generate a Python script to distribute a marketing email. The resulting code caused the recipients' email addresses to be visible to everyone, affecting a total of 95,364 customers.
"The incident was caused by a human error in developing the email distribution code with an AI tool," the PDPC said in response to queries from CNA.
According to a statement posted on its website on Sep 21, PDPC said the incident was "not a malfunction in the AI tool", but a result of the prompt given to it by the employee.
CNA Games Guess Word Crack the word, one row at a time Buzzword Create words using the given letters Mini Sudoku Tiny puzzle, mighty brain teaser Mini Crossword Small grid, big challenge Word Search Spot as many words as you can Show More Show Less PDPC said the employee had prompted the AI tool to write a programme to send a "mass email using a local list" in batches, without specifically telling it to hide the email addresses of the other recipients.
"The employee did not realise the error before deploying the script, as testing was done by checking activity logs without reviewing the contents of the actual test email," said PDPC.
It added that the affected data "was not managed, processed, or generated by any AI-powered operation or process", and that there was "no evidence of further misuse" of the data.
The PDPC noted that Bee Cheng Hiang took prompt remedial actions, including immediately stopping the bulk marketing email distribution process, correcting the erroneous script and informing affected customers.
The company also introduced a requirement for at least two staff members to verify all bulk email communications.
The PDPC noted that this is Bee Cheng Hiang's first attempt at incorporating AI tools into its business operations.
"Prior to adopting AI tools to enhance the efficiency of their business operations, organisations should carry out appropriate data protection impact assessments; develop policies and processes; and implement testing and review mechanisms, to ensure that their employees use AI tools responsibly and safeguard personal data."
Taking into account the circumstances of the case, the PDPC accepted a voluntary undertaking from Bee Cheng Hiang to improve its compliance with the Personal Data Protection Act.